Microsoft cloud security for organisations that have to pass the audit.
Conditional Access
Rolling out Conditional Access without locking out your staff
Conditional Access decides who gets into Microsoft 365. This article sets out a safe rollout sequence: inventory, emergency access accounts, report-only mode, a pilot group and the evidence your auditor will ask for.
Detecting and stopping AI-powered attacks: what works in Microsoft 365
AI makes phishing flawless, voices easy to fake and attacks faster. Effective defence does not depend on staff spotting the fake. The five measures in Entra ID and Defender to start with, and how these attacks show up in your signals.
Conditional Access and passkeys: how to move to phishing-resistant sign-in
Microsoft is making passkeys the default in Entra ID and retiring SMS and voice as sign-in methods. This article covers the available methods, how to enforce them with Conditional Access and the order in which the migration works.
How to tell if your IT provider runs Microsoft 365 securely
Ten pieces of evidence a good IT provider or internal IT team can produce within a day: from MFA coverage and Conditional Access to DMARC, backups and the monthly report. With guidance on what a good answer looks like.
Email security with Microsoft 365, part 1: setting up SPF, DKIM and DMARC correctly
SPF, DKIM and DMARC are basics, yet they are misconfigured again and again. What the three DNS records do, what happens without them, and how to implement them properly in Exchange Online.
Email security with Microsoft 365, part 2: getting Defender for Office 365 right
Many organisations already pay for Microsoft Defender for Office 365 but run it on defaults. What each protection feature does, which misconfigurations we see most often and how to evidence the protection.
Using Global Secure Access to control which AI tools are used in your organisation
AI bans are rarely followed. How to allow approved AI tools with Microsoft Entra Internet Access, make the rest visible or block it, and produce evidence an auditor will accept.
How to make AI adoption succeed with Entra ID, Purview, SharePoint and OneDrive
Microsoft 365 Copilot and Claude surface whatever a user can already access. The real risk is oversharing. The steps in Entra ID, SharePoint and Purview that belong before the roll-out.
What Microsoft Entra Agent ID is and how it fits into existing services
AI agents act with permissions, so they need identities, accountable owners and a lifecycle. What Microsoft Entra Agent ID provides, how it works with Conditional Access and ID Governance, and what to do now.
Defender for Endpoint: detecting and blocking prompt injection in local AI agents
AI agents such as Claude Code or GitHub Copilot CLI work with the permissions of the person at the keyboard. Microsoft Defender for Endpoint can detect and block injected instructions at runtime. What the feature does, what it requires and how to roll it out.
DORA in the Microsoft cloud: what financial entities must implement and evidence
DORA has applied since 17 January 2025. What the regulation requires, what role Microsoft plays as an ICT third-party service provider, and how to maintain evidence with Purview Compliance Manager, Sentinel and Defender.
Zero Trust explained: an adoption guide for businesses
Zero Trust is an architectural principle. This article explains the concept and shows how to implement it step by step with Entra ID, Intune, Defender, Sentinel and Purview.
NIS2 in Germany: implementing the obligations and proving them with Microsoft 365
The German NIS2 implementation act has applied since 6 December 2025. Who is in scope, which obligations and reporting deadlines apply, and how to implement and evidence the measures with Entra ID, Defender, Sentinel and Intune.
AI and cybersecurity in Microsoft environments: Security Copilot, AI phishing and Copilot adoption
Three concrete topics instead of buzzwords: what Microsoft Security Copilot offers a small security team, what works against AI-generated phishing, and which risks to settle before rolling out Microsoft 365 Copilot.
Securing Microsoft Entra ID for mid-sized businesses
Entra ID controls access to Microsoft 365 and Azure, which makes it a prime attack target. This article shows which measures protect your identities: MFA, permissions, Conditional Access and log analysis.
Finding, preventing and evidencing misconfigurations in Azure
Which Azure misconfigurations we check first in an assessment, and how to fix them permanently and document them as evidence with Microsoft Defender for Cloud, Azure Policy and a landing zone.
Cyber insurance: evidencing insurer requirements with Microsoft 365
What cyber insurers typically ask about MFA, EDR, patching, backup and logging, and which reports from Entra ID, Defender, Intune and Azure Backup evidence your answers.
Ransomware preparedness in Microsoft environments: Why backups alone are not enough
Backups are necessary but not sufficient. How to harden endpoints with Defender for Endpoint and Intune, protect administrator accounts, and make backups in Azure Backup and Microsoft 365 Backup tamper-resistant.
Defender XDR and Microsoft Sentinel: When is XDR enough, and when do you need Sentinel?
What Microsoft Defender XDR covers at no extra cost, what Microsoft Sentinel adds, how the cost logic works, and which operating model has to stand behind “someone is watching the alerts”.
Incident response in the Microsoft 365 tenant: What companies should prepare
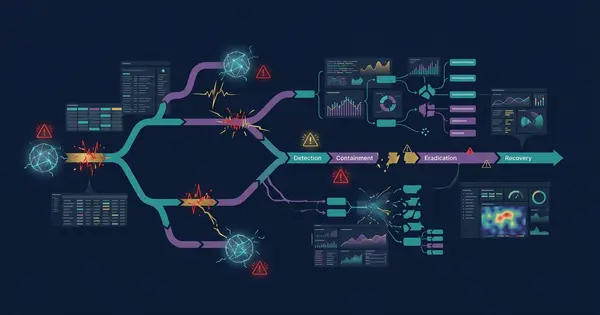
Which decisions management has to make before an incident, what IT does in the first hour after an account takeover in Entra ID, and which evidence counts for NIS2 and insurers.